Cloud Based Data Security: 4 Core Pillars, Shared Responsibility, and Enterprise Training
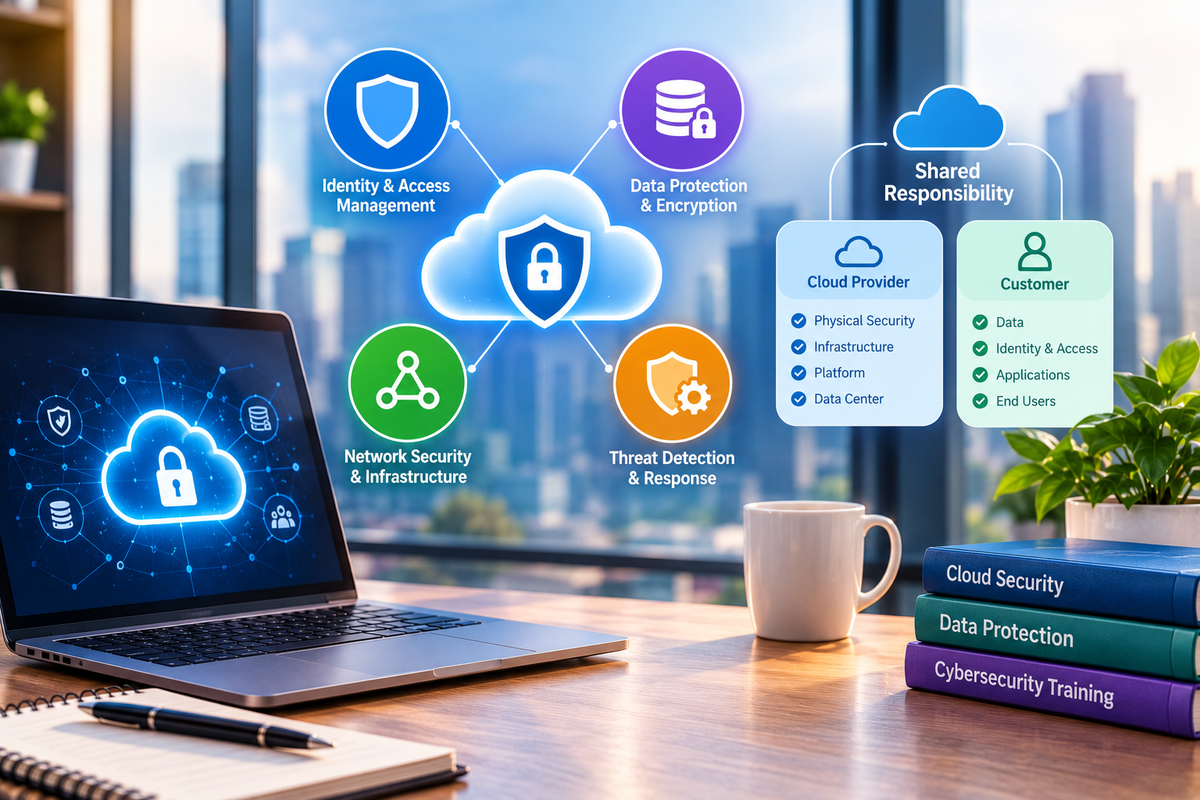
As modern enterprises accelerate multi-cloud migrations across AWS, Microsoft Azure, and Google Cloud, cloud based data security has transitioned from a routine IT concern to an urgent board-level priority. Cloud environments offer unprecedented operational scalability, but they also dismantle the traditional network perimeter.
When critical infrastructure, customer records, and proprietary databases reside across distributed hybrid setups, securing your enterprise requires moving beyond basic firewalls to a comprehensive data-centric strategy.
The Evolving Cloud Threat Landscape
In traditional on-premises IT setups, security teams relied on defensive boundaries to keep external threats out. In cloud-native environments, the network perimeter is fluid and dynamic. Modern threat vectors exploit internal configuration gaps rather than brute-forcing network perimeters:
- Cloud Misconfigurations: The majority of cloud security incidents stem from operational oversights such as publicly accessible storage buckets, unsegmented virtual networks, and unmonitored API endpoints.
- Over-Privileged Access: Excessively permissive Identity and Access Management (IAM) policies allow lateral movement during a breach, enabling attackers to escalate privileges.
- Shadow Cloud Deployment: Departments often spin up unvetted third-party SaaS platforms or cloud storage instances without IT oversight, exposing sensitive data to compliance risks.
Understanding the Shared Responsibility Model
A frequent point of failure in enterprise cloud migrations is assuming that the cloud service provider (CSP) handles all security management. Operating safely requires a clear understanding of the Shared Responsibility Model.
| Security Domain | Cloud Service Provider (CSP) | Enterprise Customer |
| Physical Infrastructure | Data centers, server hardware, power, physical security | None |
| Hypervisor & Core Network | Infrastructure virtualization, physical network maintenance | None |
| Guest OS & Networking | Managed services only (PaaS / SaaS) | Virtual network configuration, firewall rules, routing |
| Data & Identity Governance | None | IAM policies, user permissions, data encryption, compliance |
- The CSP's Job: Securing the underlying physical and virtual foundation ("Security of the Cloud").
- Your Job: Securing access controls, application code, network settings, and data assets ("Security in the Cloud").
The 4 Core Pillars of Cloud Based Data Security
To prevent data exfiltration, ransomware attacks, and compliance failures, enterprise technology leaders must structure their defense around four foundational pillars:
1. Zero Trust Architecture (ZTA)
Zero Trust operates under a single principle: Never trust, always verify. Every user, device, and service request must be continuously authenticated and authorized, regardless of whether the request originates inside or outside the corporate network.
- Enforce Least Privilege Access Control through granular Role-Based Access Control (RBAC).
- Mandate Multi-Factor Authentication (MFA) across all management consoles, access keys, and VPNs.
- Apply continuous micro-segmentation to isolate workloads and prevent lateral movement during a breach.
2. Multi-Layered Data Encryption
Encrypting sensitive data ensures that even if perimeter controls are bypassed, exfiltrated files remain unreadable and useless to bad actors.
| Data State | Threat Vector | Required Protection |
| Data at Rest | Unauthorized access to storage buckets or database backups | AES-256 encryption with customer-managed keys (KMS / HSM) |
| Data in Transit | Interception across public networks and internal APIs | TLS 1.3 enforcement and dedicated encrypted interconnects |
| Data in Use | Memory inspection during active processing | Confidential Computing using trusted hardware execution environments |
3. Identity and Access Management (IAM) Governance
Identity is the new security perimeter in cloud architecture. Effective IAM governance requires regular privilege audits, automated access revocation for departing employees, and temporary, time-bound credentials for administrative tasks rather than permanent root keys.
4. Continuous Cloud Security Posture Management (CSPM)
Because cloud infrastructure is constantly modified through automated pipelines and manual adjustments, static annual security audits are insufficient. CSPM tools provide automated, real-time visibility into cloud configurations, detecting security drift, compliance violations (such as ISO 27001, SOC 2, and GDPR), and misconfigurations before they can be exploited.
Bridge the Enterprise Security Gap with CourseMonster
Building robust cloud based data security requires more than just deploying security tools it requires certified, highly skilled engineers who know how to configure, audit, and manage those tools effectively.
At CourseMonster, we provide specialized enterprise upskilling programs designed to bring your technical teams up to speed on modern cloud protection frameworks:
Course Highlights: Enterprise Cloud Security & Data Governance
- Hands-on Configuration: Real-world labs in AWS, Azure, and GCP security tools.
- IAM & Zero Trust Design: Architecting secure access frameworks and micro-segmented networks.
- Compliance & Auditing: Aligning cloud configurations with ISO 27001, NIST, and SOC 2 standards.
- Incident Response: Practical simulations for detecting misconfigurations and mitigating live threat scenarios.
Powered by Course Leagues for Guaranteed Completion
To ensure your team completes their training on schedule, CourseMonster courses integrate Course Leagues our enterprise team-based accountability platform. Your engineers learn together in structured cohorts, complete weekly sprint milestones, track progress on live leadership dashboards, and earn verifiable skill badges.
Protect your enterprise infrastructure with certified expertise. Contact CourseMonster today to explore our Cloud Security Course catalog and build a tailored training roadmap for your team.


Comments ()